One platform for every
security finding you have.
Offload connects your cloud accounts, repositories, container registries, Kubernetes clusters, applications and existing security tools. It normalizes and de-duplicates their findings into one data model, prioritizes the risk, tracks remediation and collects compliance evidence, all from a single platform you run on your own infrastructure or use as SaaS.

 CloudPositive
Take the tour — no demo required.
The same views your team gets on day one: posture, findings, attack paths, compliance and threat context — one data model behind all of them.
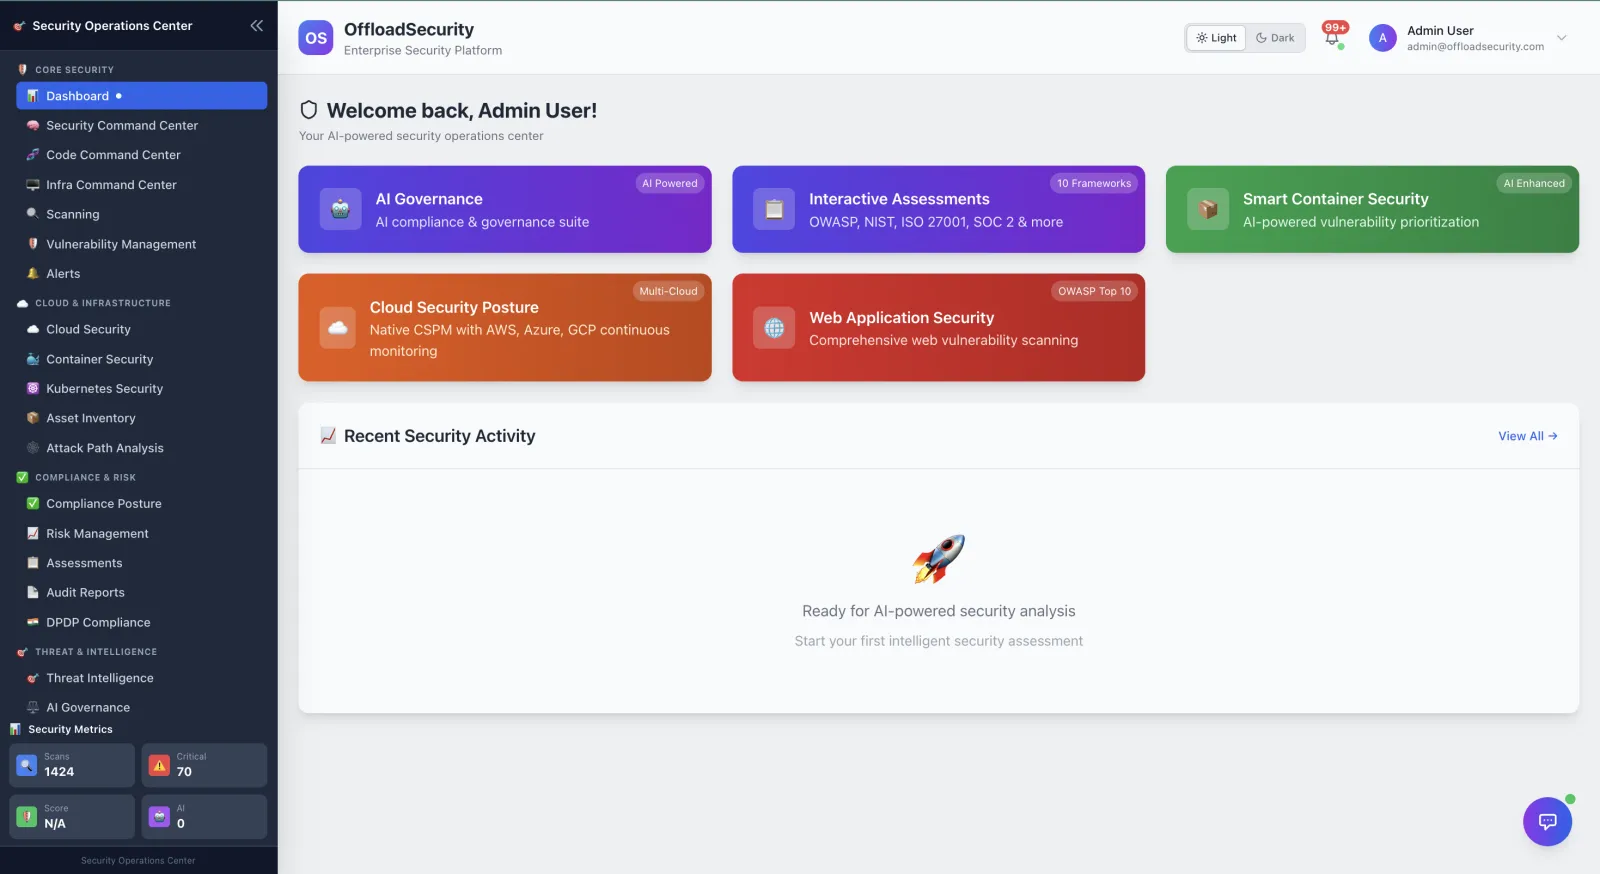
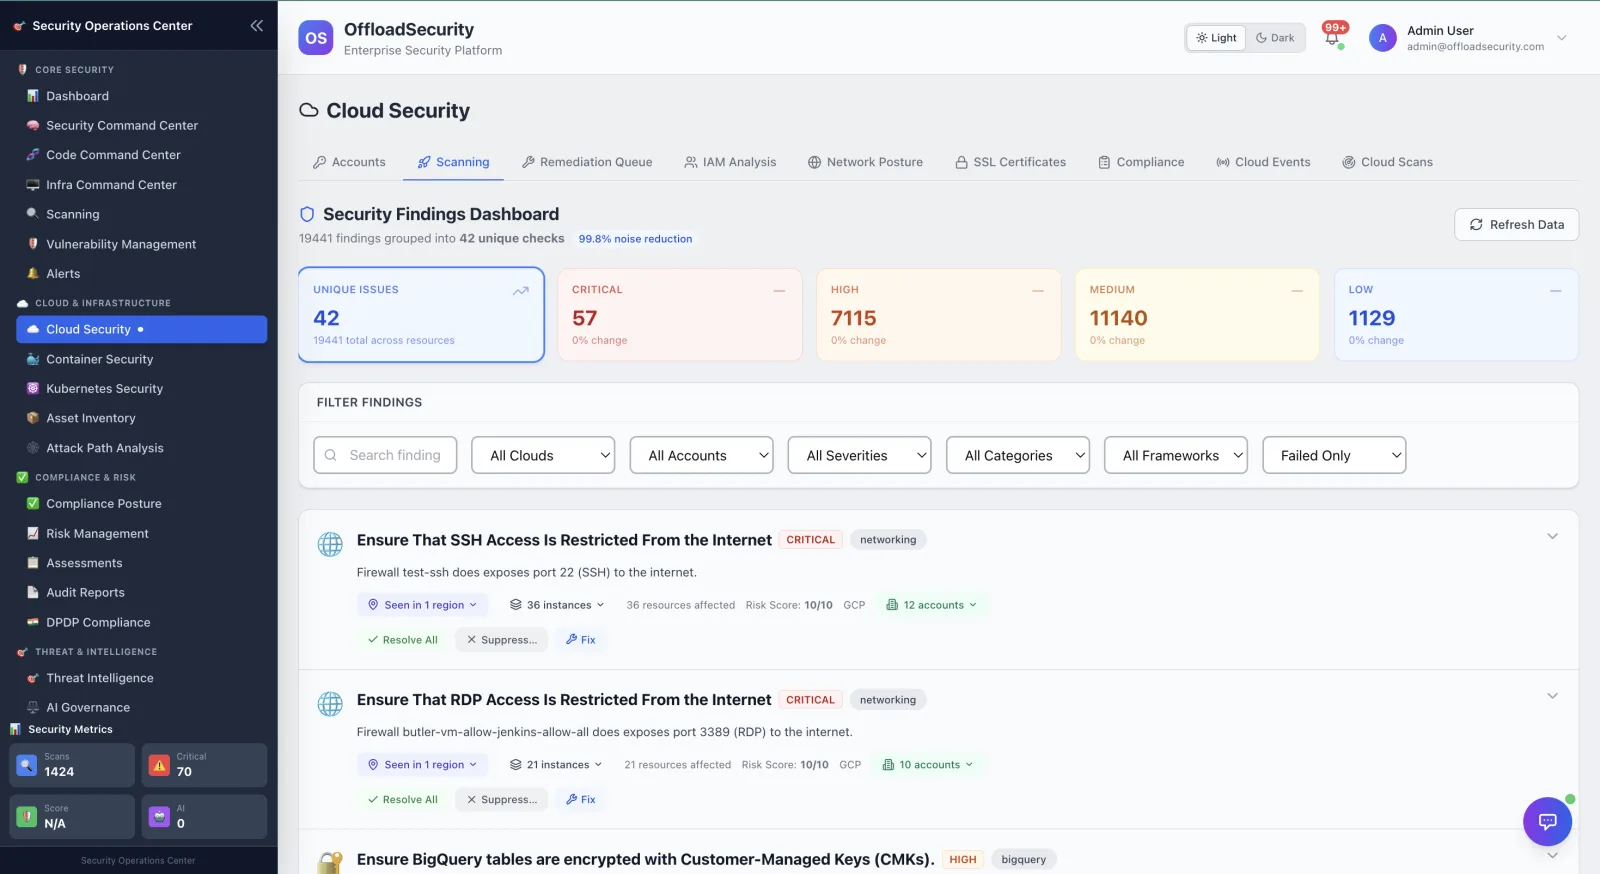
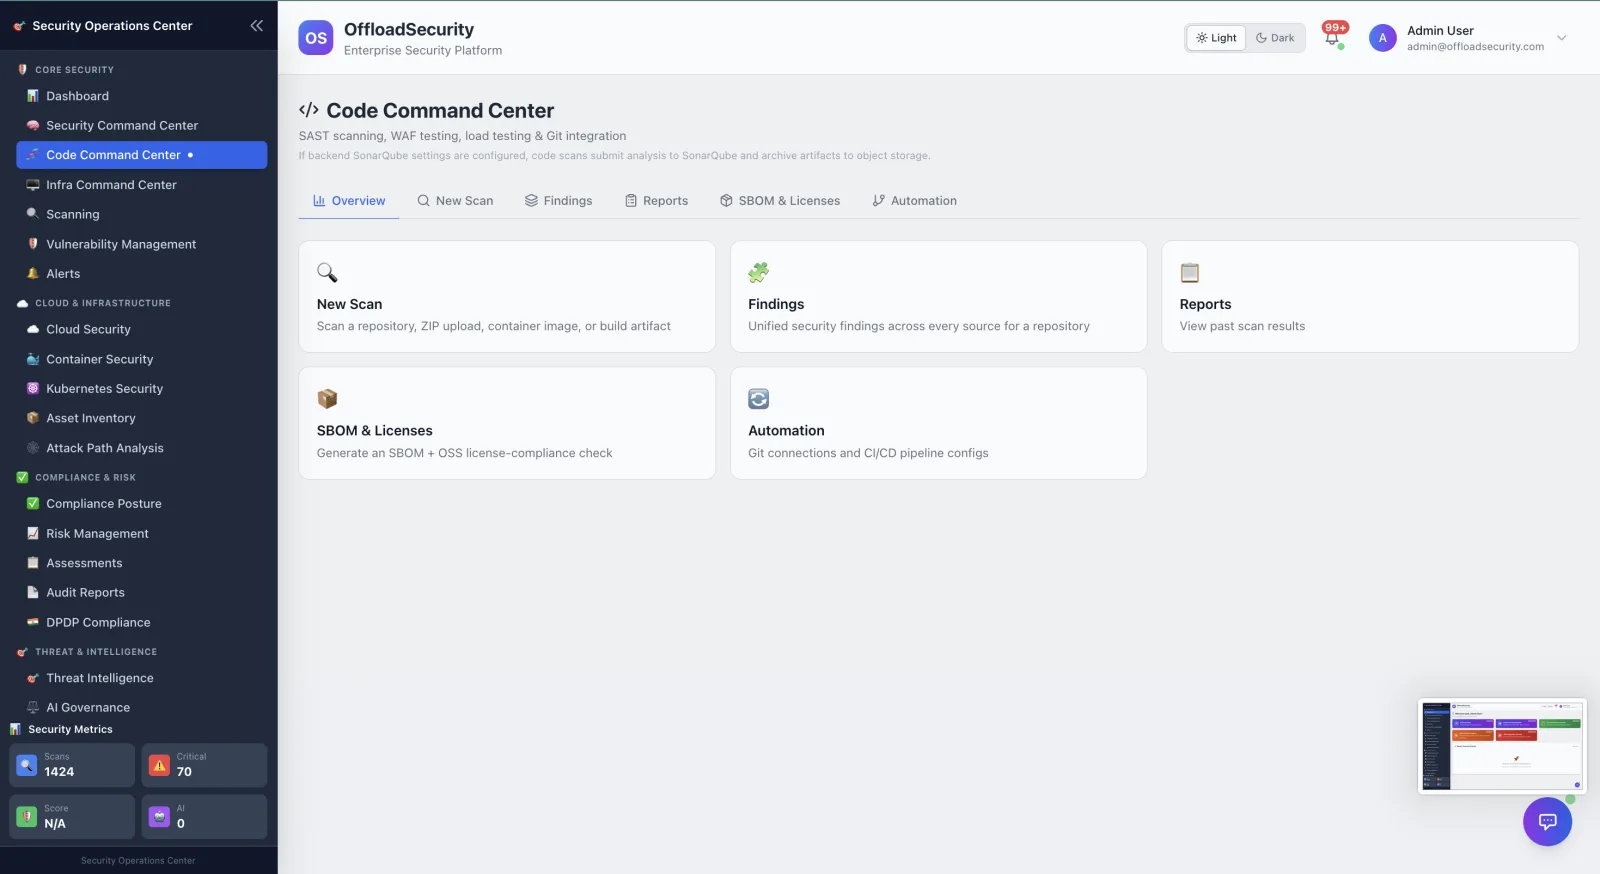
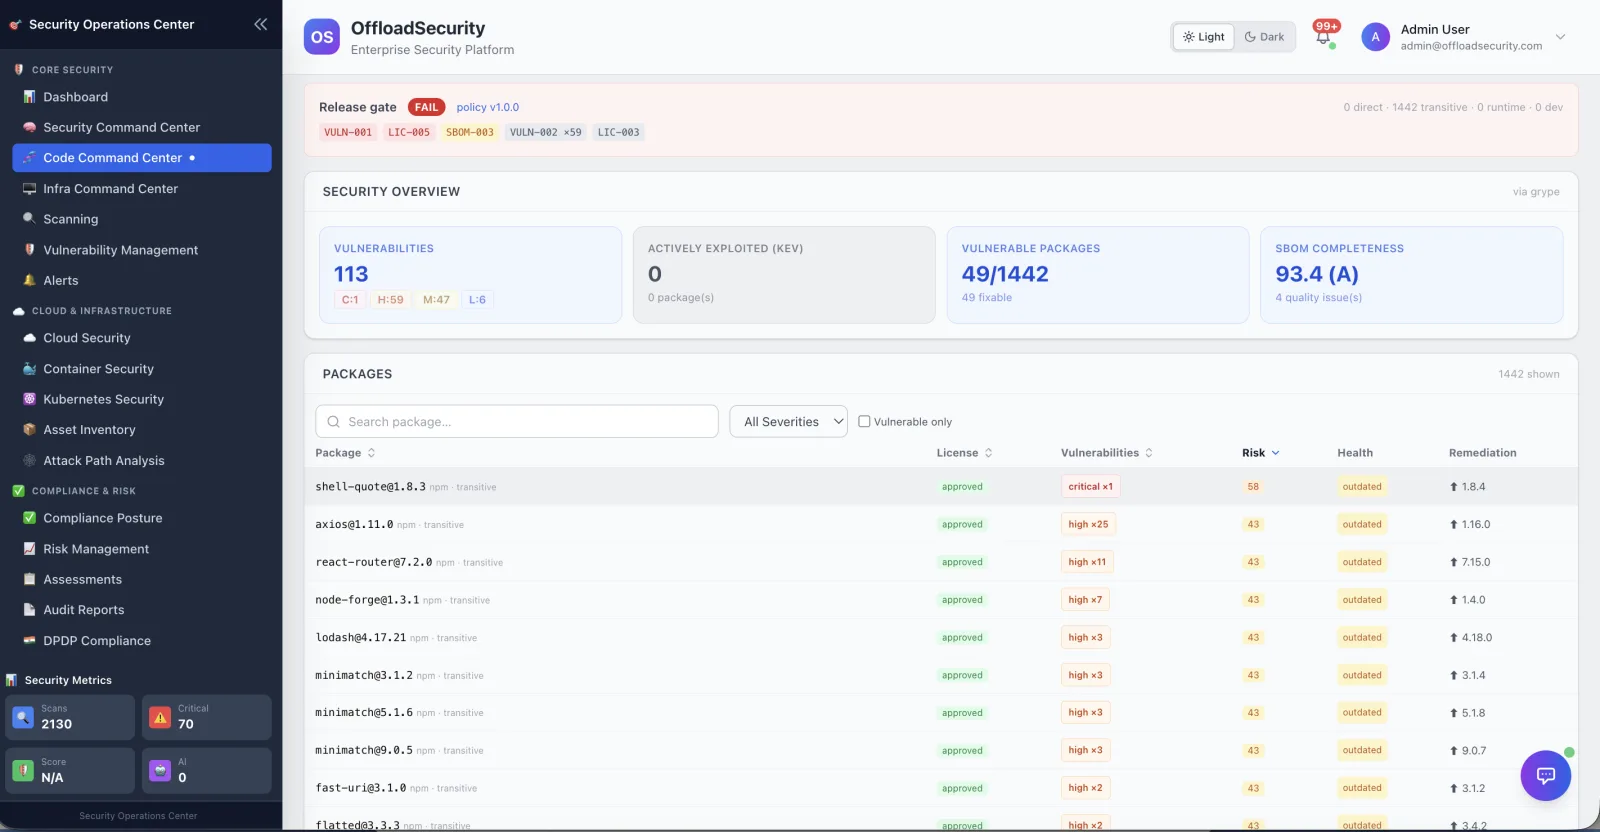
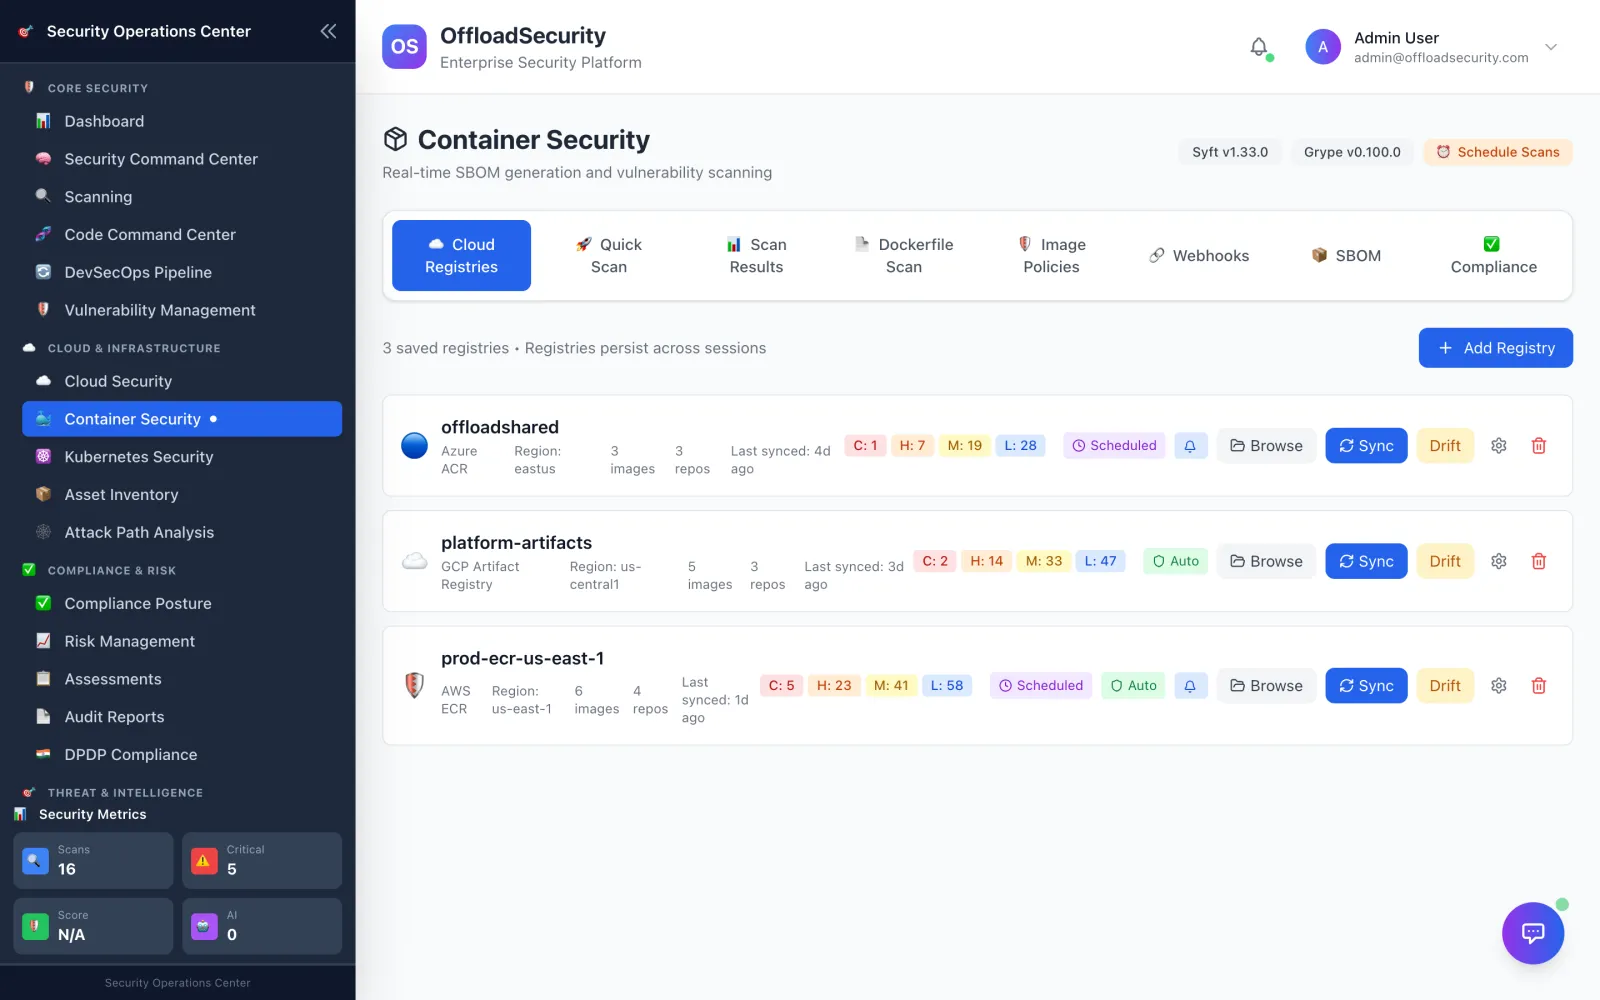
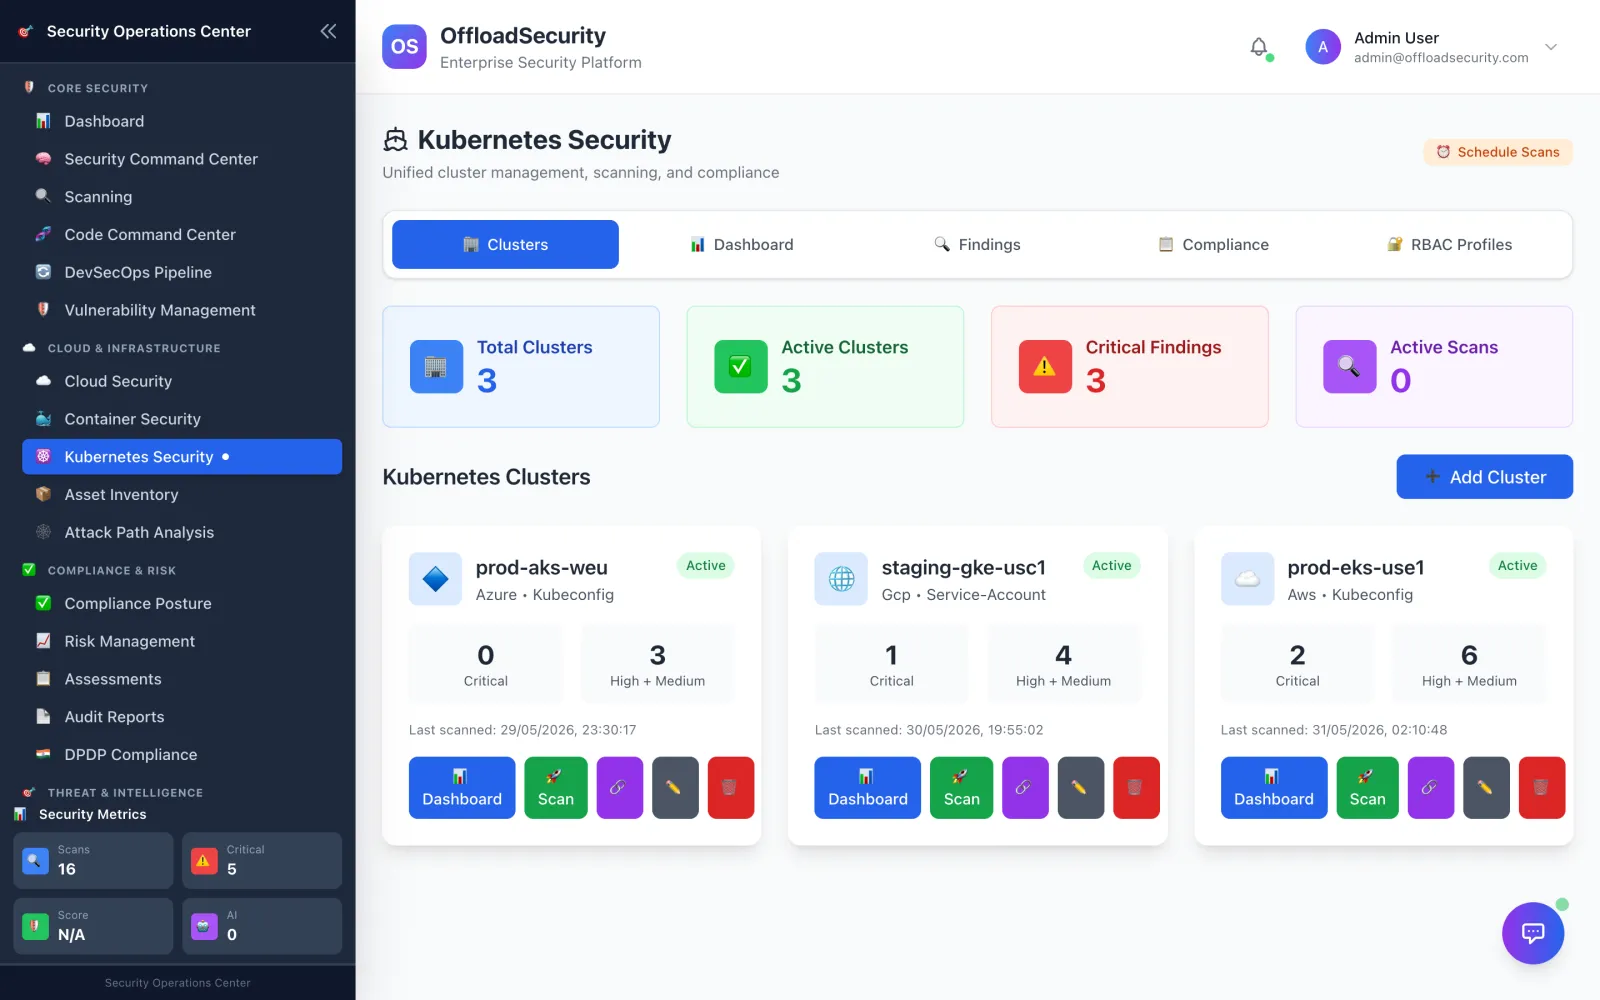
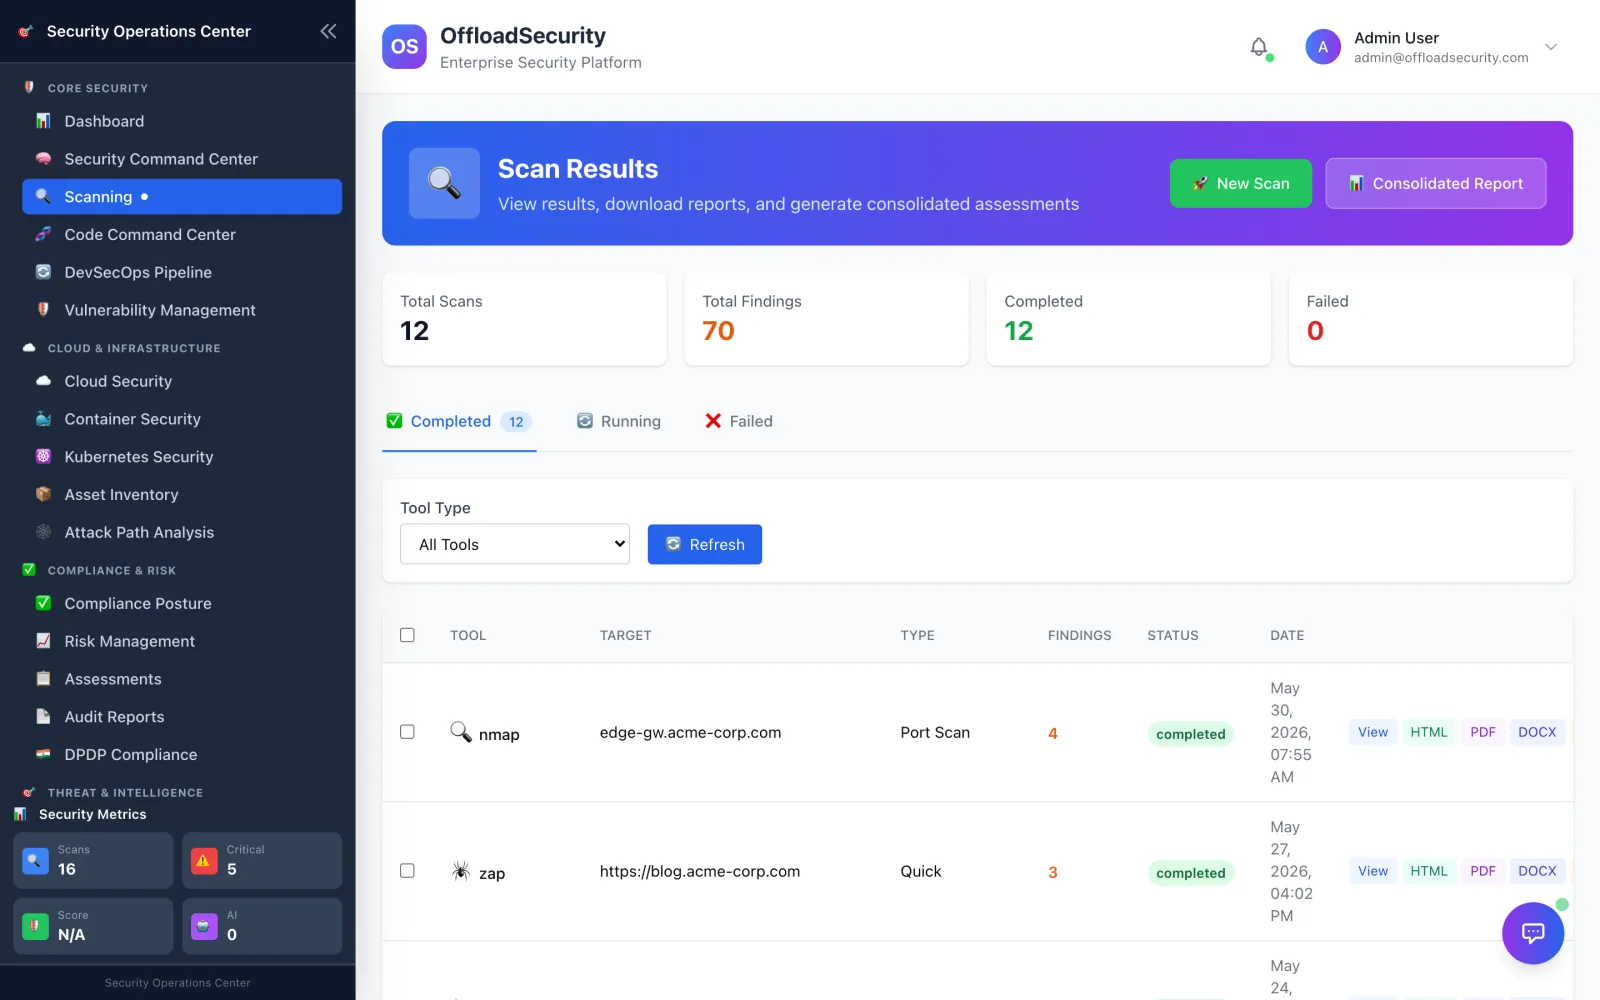
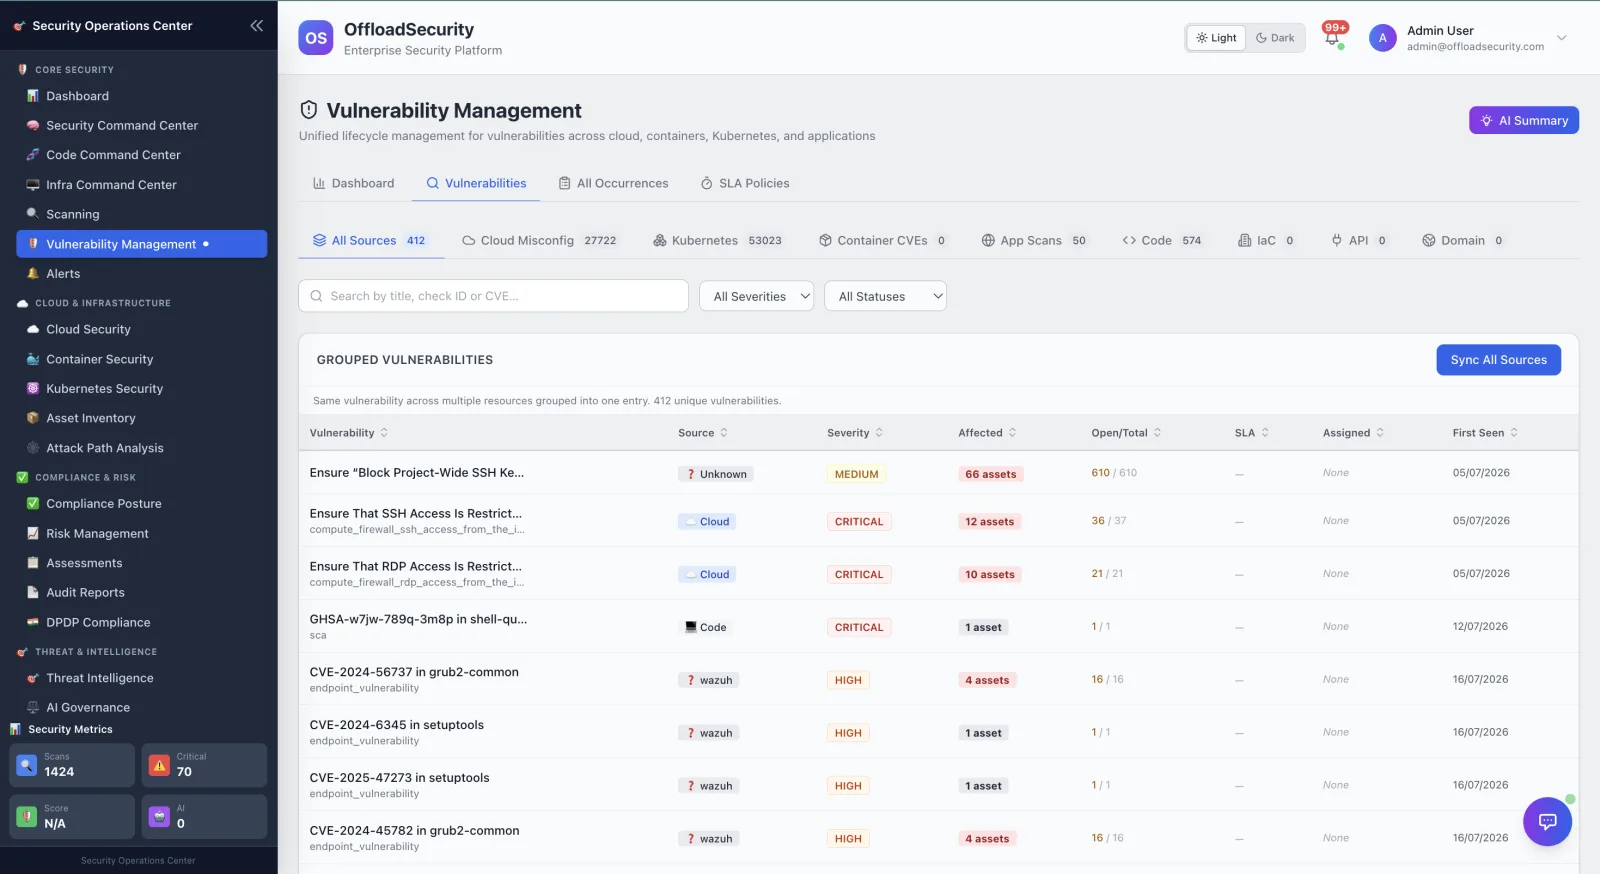
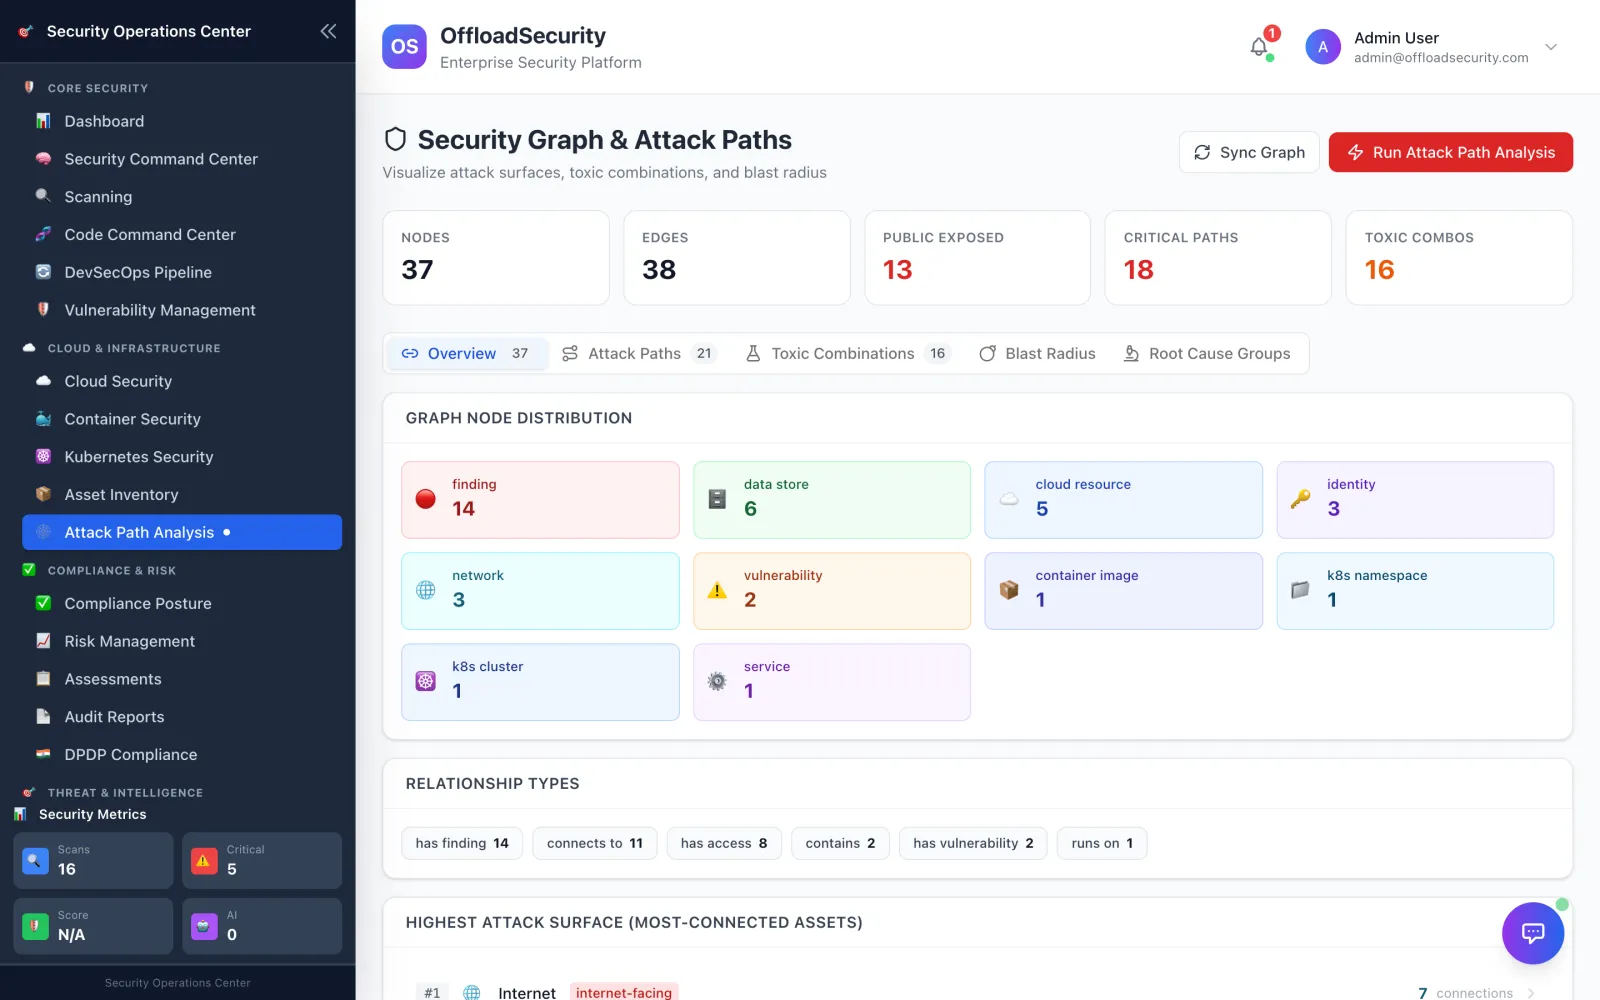
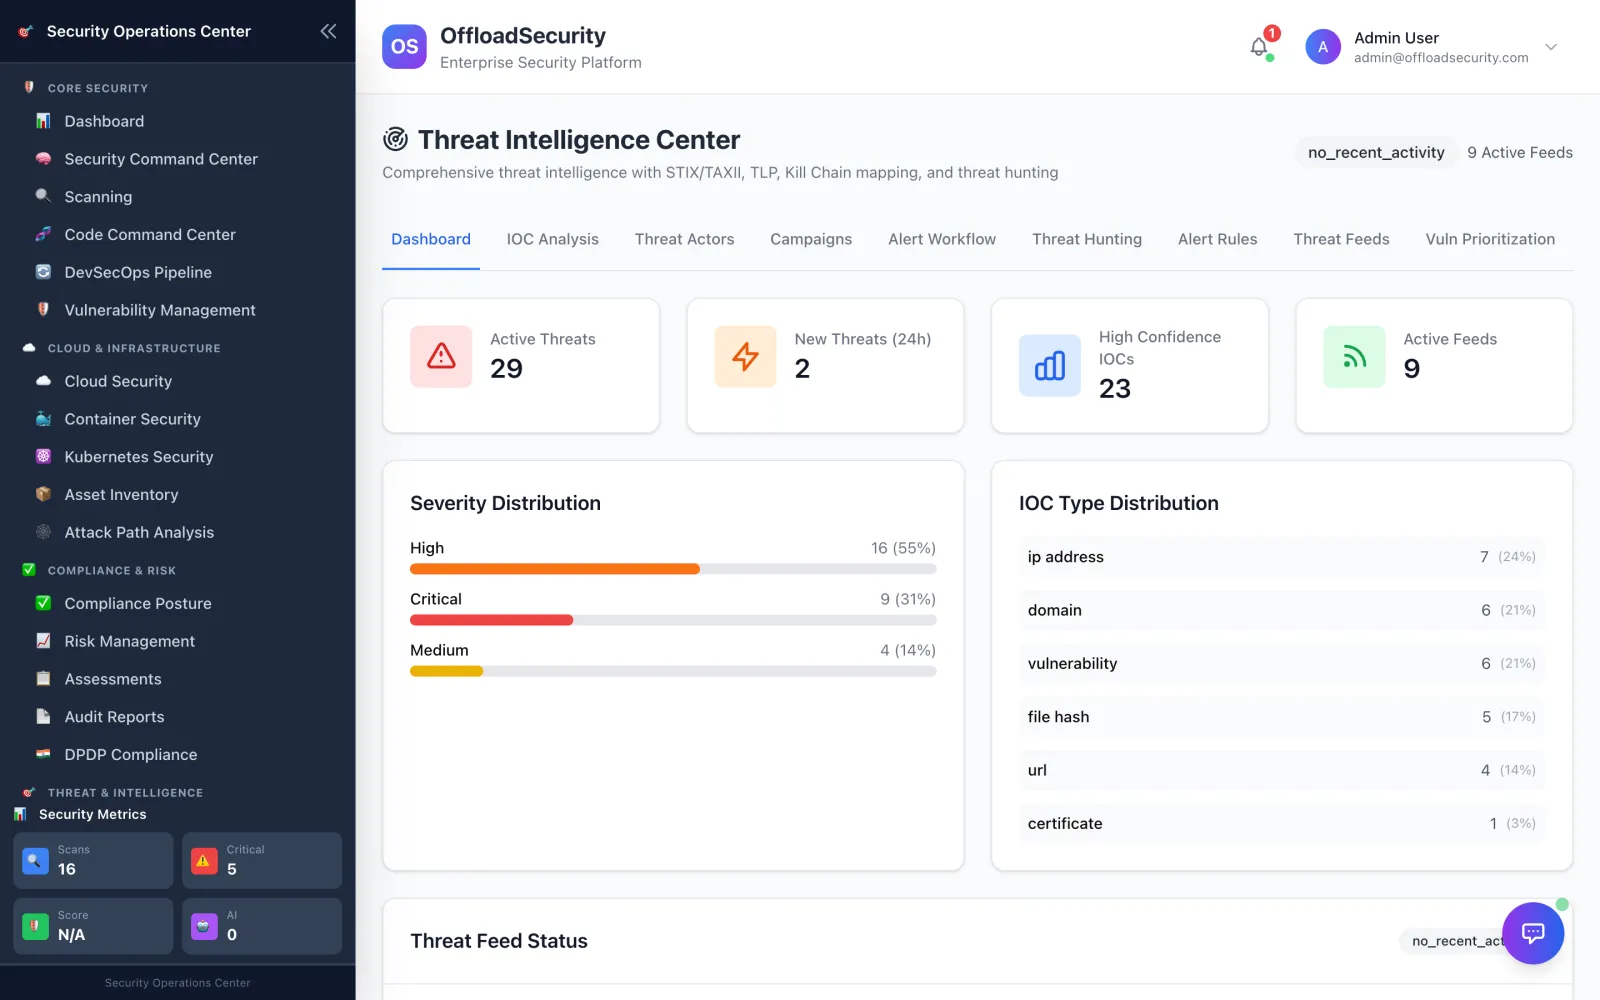
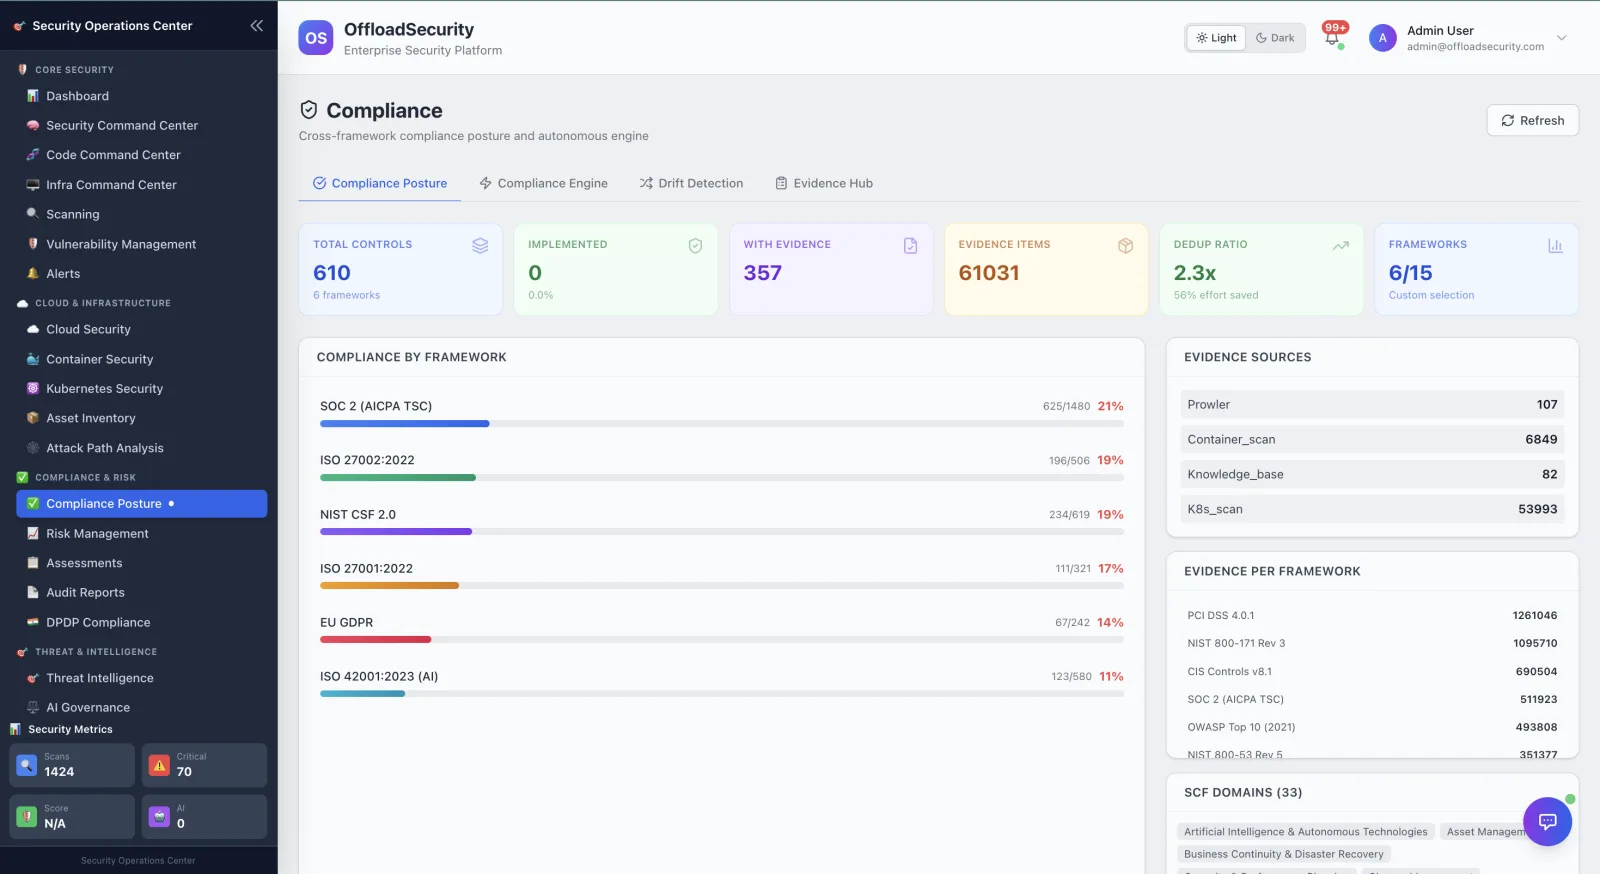
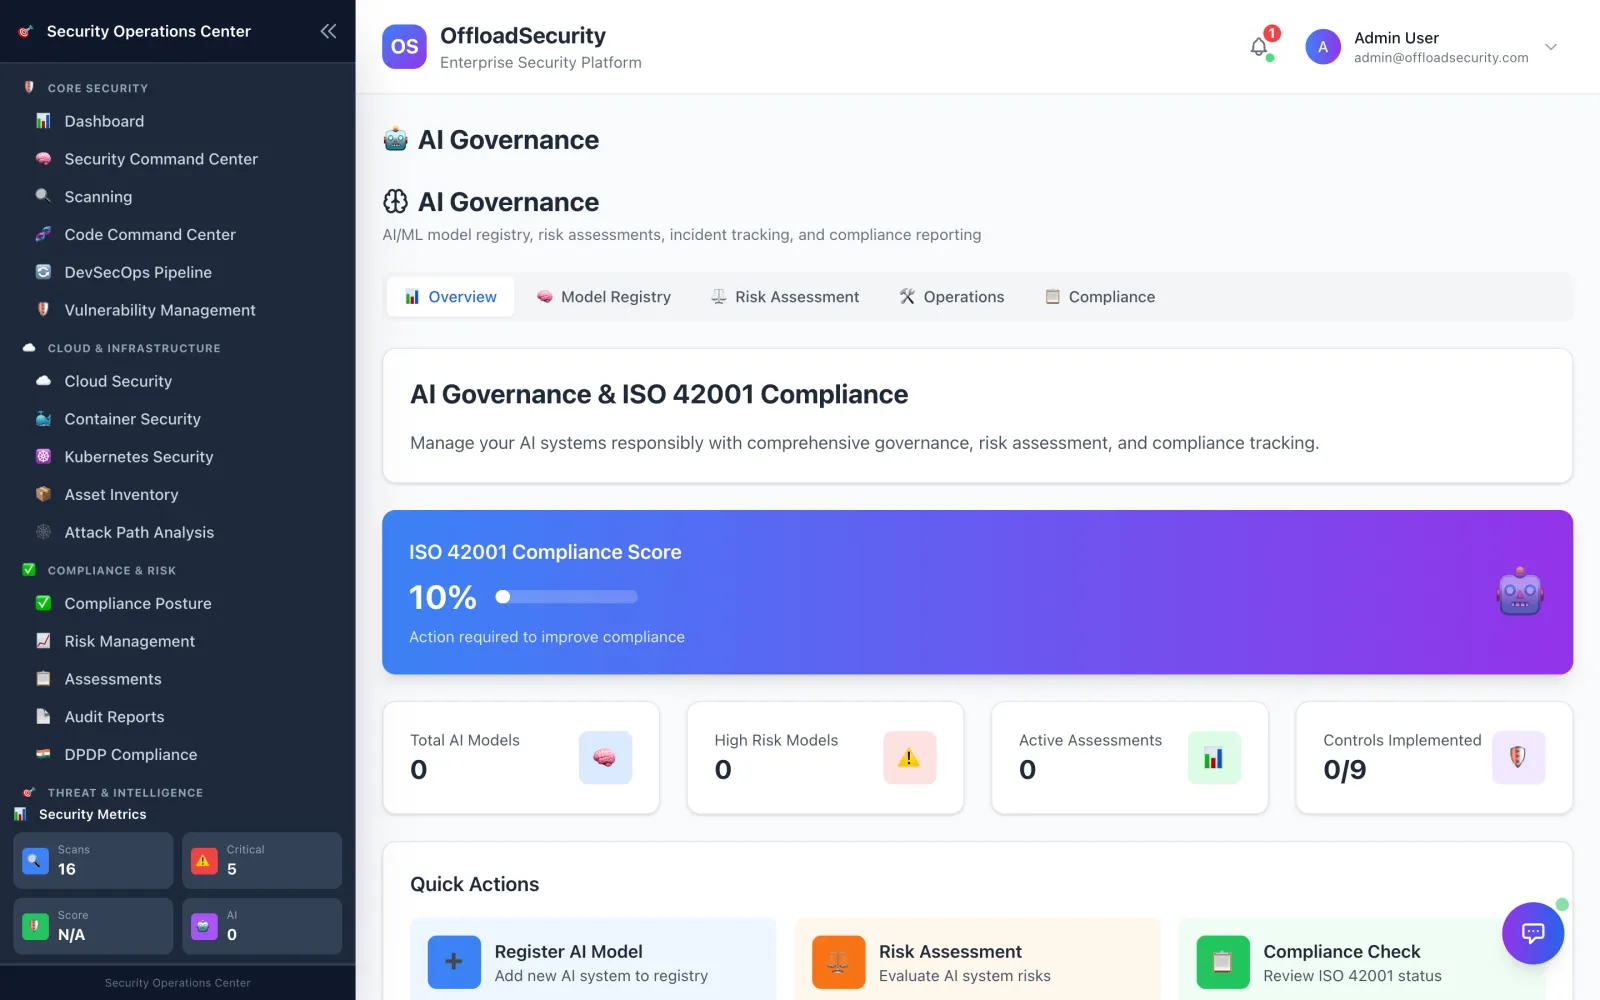
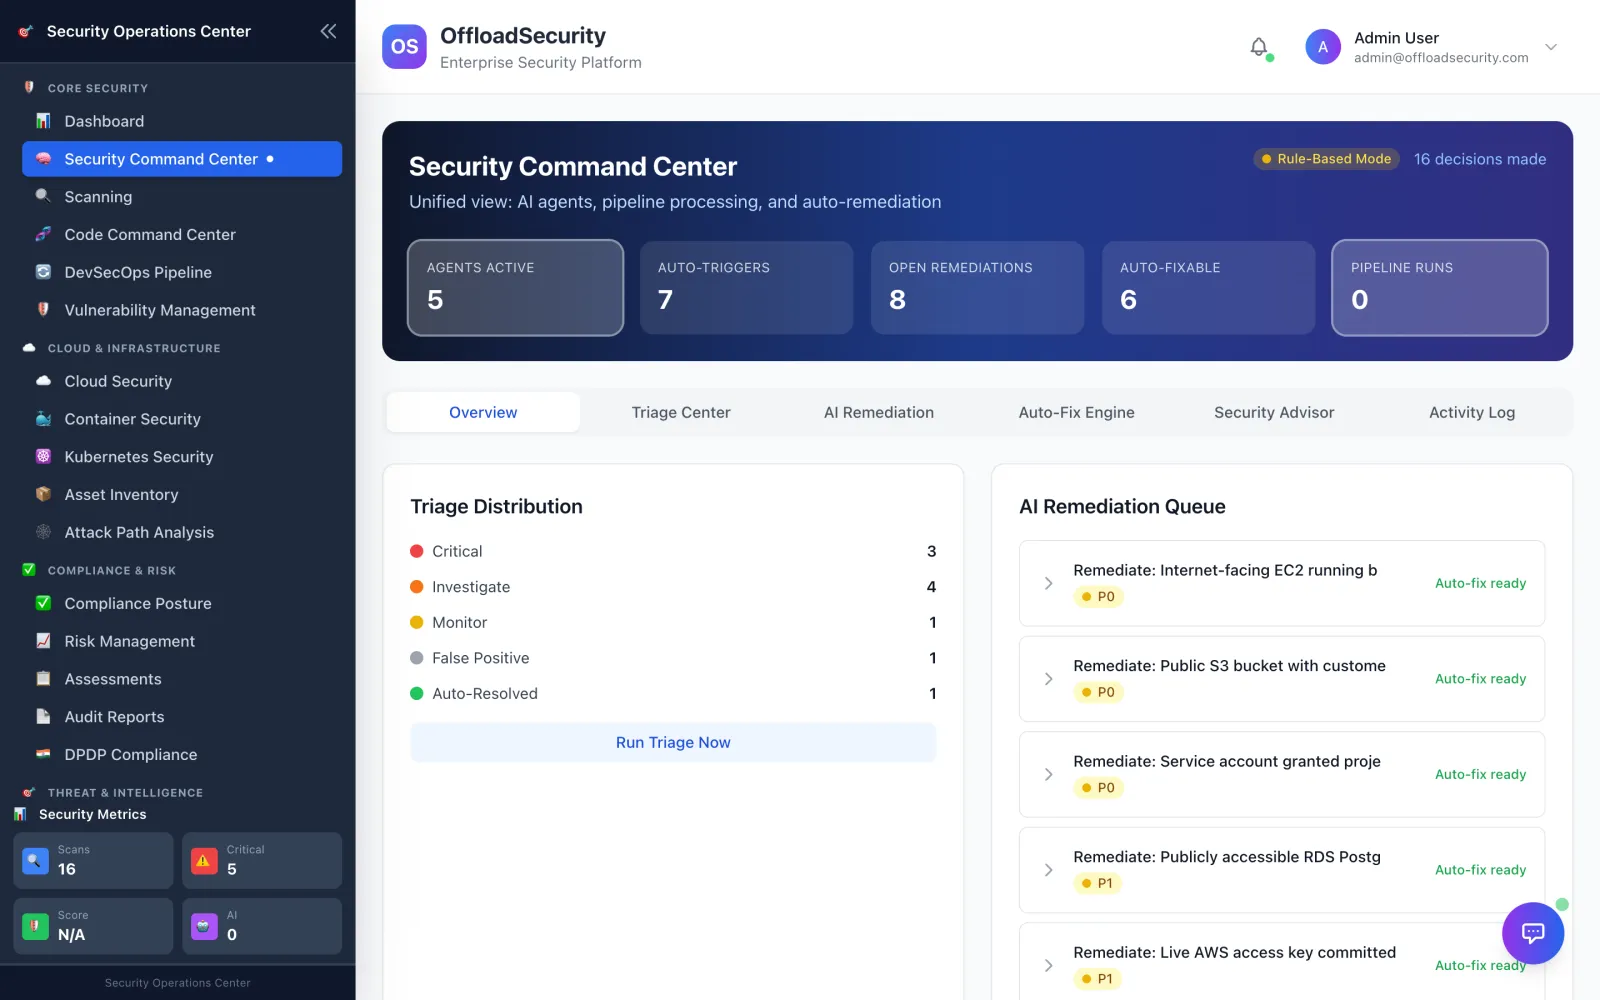
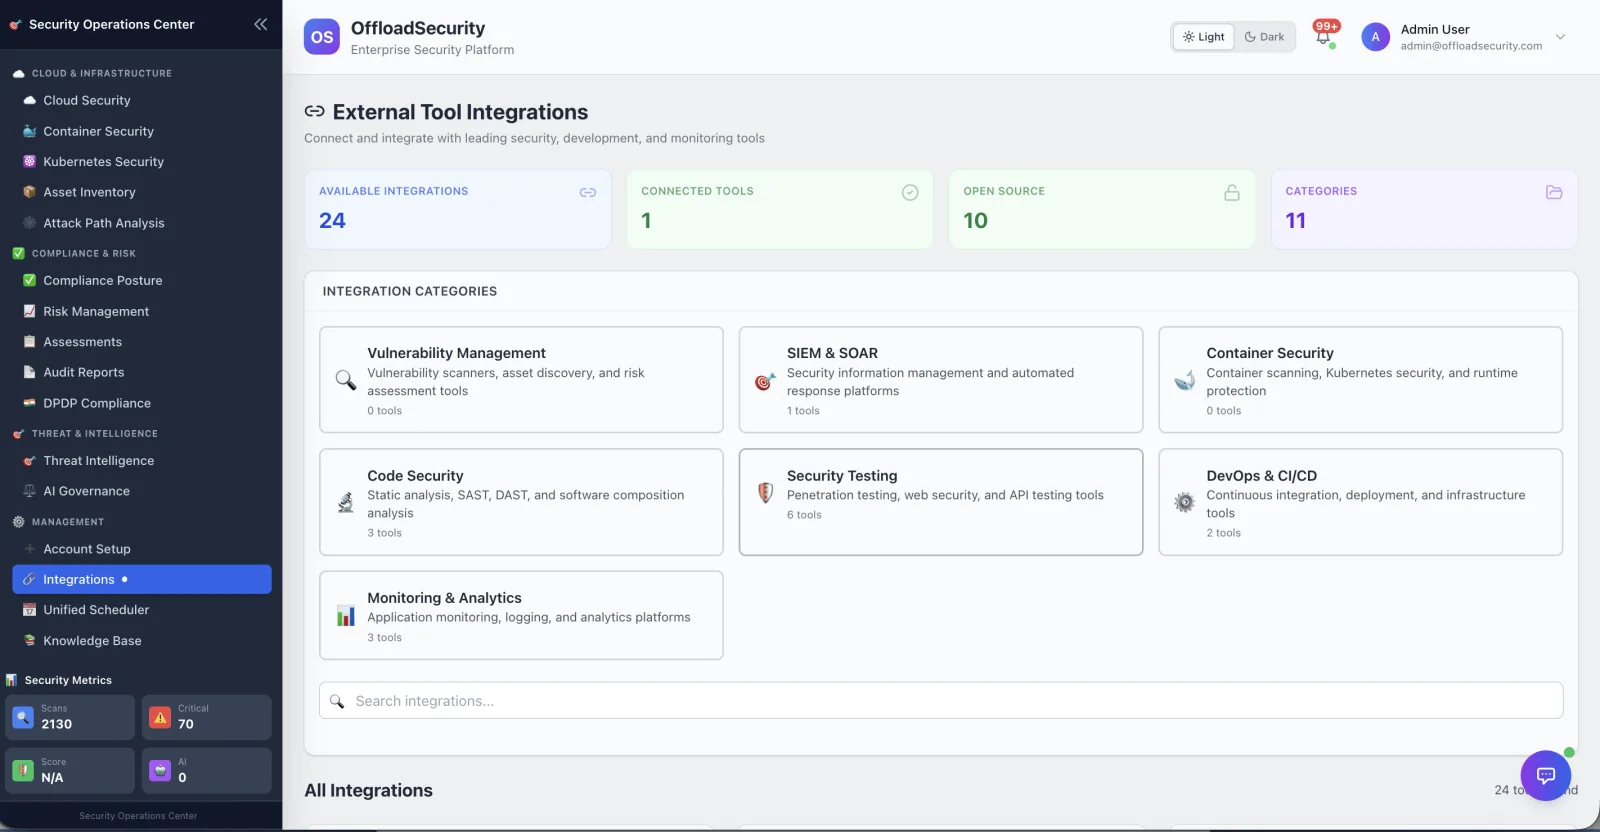
One dashboard — risk score, engine status, severity breakdown and the top critical findings across every domain.
Security findings live in ten consoles and one overworked spreadsheet.
Fragmented tools
Scanner sprawl across cloud, code, containers, and clusters — each with its own console, severity scale, and export format.
Manual consolidation
Findings collected, de-duplicated, and reported by hand before remediation can even start. The team spends its time preparing data instead of reducing risk.
Compliance in a parallel universe
Risk registers and compliance dashboards disconnected from technical reality — green on paper, unknown in production.
The questions your tools leave open.
Point solutions each answer a slice. Offload answers the question that actually matters — with the evidence to back it.
Which of our exposures are actually being exploited?
Threat intelligence enriches every finding with CISA KEV and EPSS, so actively-exploited issues rise above theoretical criticals.
KEV + EPSS on every finding
Which risks actually reach our crown jewels?
Identity-aware attack-path analysis maps the routes an attacker would really take — and pinpoints the choke points that cut the most paths.
Choke-point & blast-radius analysis
Is our running web app and API actually exploitable?
A dedicated DAST suite tests the live application and its APIs — authenticated — in one orchestrated pass, with a single graded report.
ZAP · Nuclei · OWASP API Top 10
Can we prove DPDP readiness on the regulator's clock?
The DPDP module runs DPIAs and SDF classification and drives a breach workflow with statutory deadline tracking.
DPB + CERT-In deadline watchdogs
Where do all our findings actually live?
One deduplicated queue across cloud, code, containers, Kubernetes, on-prem and the tools you already run — SaaS or fully self-hosted.
One occurrence model, one severity scale
Are the AI models we ship actually secure?
AI-SPM discovers the AI models in your estate, classifies their risk, and tests them for prompt injection.
EU AI Act tiers · prompt-injection testing
Every security domain. One data model.
Each module is strong alone — together they share one finding lifecycle, one risk register, and one compliance evidence trail.
Cloud & Infrastructure
3 modulesApplication & Supply Chain
3 modulesCode Security
SAST, dependencies, secrets, IaC — governed from commit to release.
Dynamic Application & API Security Testing (DAST)
Test running web apps and APIs the way an attacker would — authenticated, in one pass.
SBOM & License Compliance
SBOM generation, analysis, and legal-grade license governance.
Vulnerability & Threat
4 modulesUnified Vulnerability Management
One queue, one lifecycle, one history — across every scanning domain.
Security Scanning & Reporting
Best-of-breed scanners, one normalized result, board-ready reports.
Threat Intelligence
Nine live feeds, IOC correlation, MITRE ATT&CK context.
Attack Path Analysis
Graph-based, identity-aware paths to your crown jewels.
Governance, Risk & Compliance
3 modulesOperations & AI
2 modulesImplementation support from the team that builds the platform.
The engineers who build Offload help you run a bounded pilot, connect your accounts, repositories and clusters, and tune the platform to your compliance program. Advik Cyber Shield LLP, the company that develops Offload, also offers independent security assessments and penetration testing as a separate service. Professional services →
Fifteen modules. One data model. One risk view.
Every scanner, integration, and threat feed converges into a single normalized finding model — then fans back out to the risk view, remediation, compliance evidence, and reporting your teams actually use.
Built different where it matters.
One platform, one data model
Replace 4–5 consoles and the spreadsheet that glues them together.
Runs in your environment
Full on-premises deployment — findings, code excerpts, and evidence never leave your control.
Compliance wired to reality
Controls backed by live findings, plus a native DPDP Act and CERT-In breach-reporting module for India.
Platform license
Not per-developer seats, not a percentage of cloud spend. Predictable consolidation economics.
See your whole risk surface in one place.
Book a 30-minute demo on your own environment, or see how Offload stacks up against the point tools you already evaluate.
Works with what you already run.
Cloud providers, source control, container registries, CI/CD, SIEM, ticketing and chat. See the documentation for setup details.
Frameworks, mapped to findings.
15 compliance frameworks and 10 auto-scored security assessments, backed by real control data — plus a dedicated DPDP Act module for India — or try the free DPDP Readiness Checker.
Priced as a platform, not a per-seat tax.
No per-developer seats, no percentage of your cloud bill. You license the platform and scope it to the estate you actually protect.
One platform license
Consolidate 4–5 tools and the spreadsheet that glues them together into a single predictable line item.
Scoped to your estate
Priced on the environments you connect — cloud accounts, repositories, clusters — not on how many people log in.
Customer-hosted or SaaS, same license
Deploy fully in your own environment with no per-seat penalty for keeping data in your control.
Tell us your estate and we'll scope a number — usually on the first call.
Built by security practitioners.
Offload Security didn't start with this platform — it started with a career spent on the other side of the pager: DevSecOps, SecOps, security engineering, and application security. The platform is that experience, productized.
Your code never leaves the scan. Your data never leaves your control.
Repositories are cloned into ephemeral scan workspaces and deleted on completion — only findings and small excerpts are retained. Credentials are encrypted at rest. Every record is tenant-isolated. Read exactly how in the Trust Center and the Source Code Protection whitepaper.
See your whole risk surface in one platform.
Take the product tour, read the documentation, or book a demo on your own environment.